github.com/owasp-noir/noir
1.3.1 / published Sep 2, 2026 / repository
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface
Hunt every Endpoint in your code, expose Shadow APIs, map the Attack Surface.


Documentation • Installation • Usage • Github Action • Contributing • Changelog
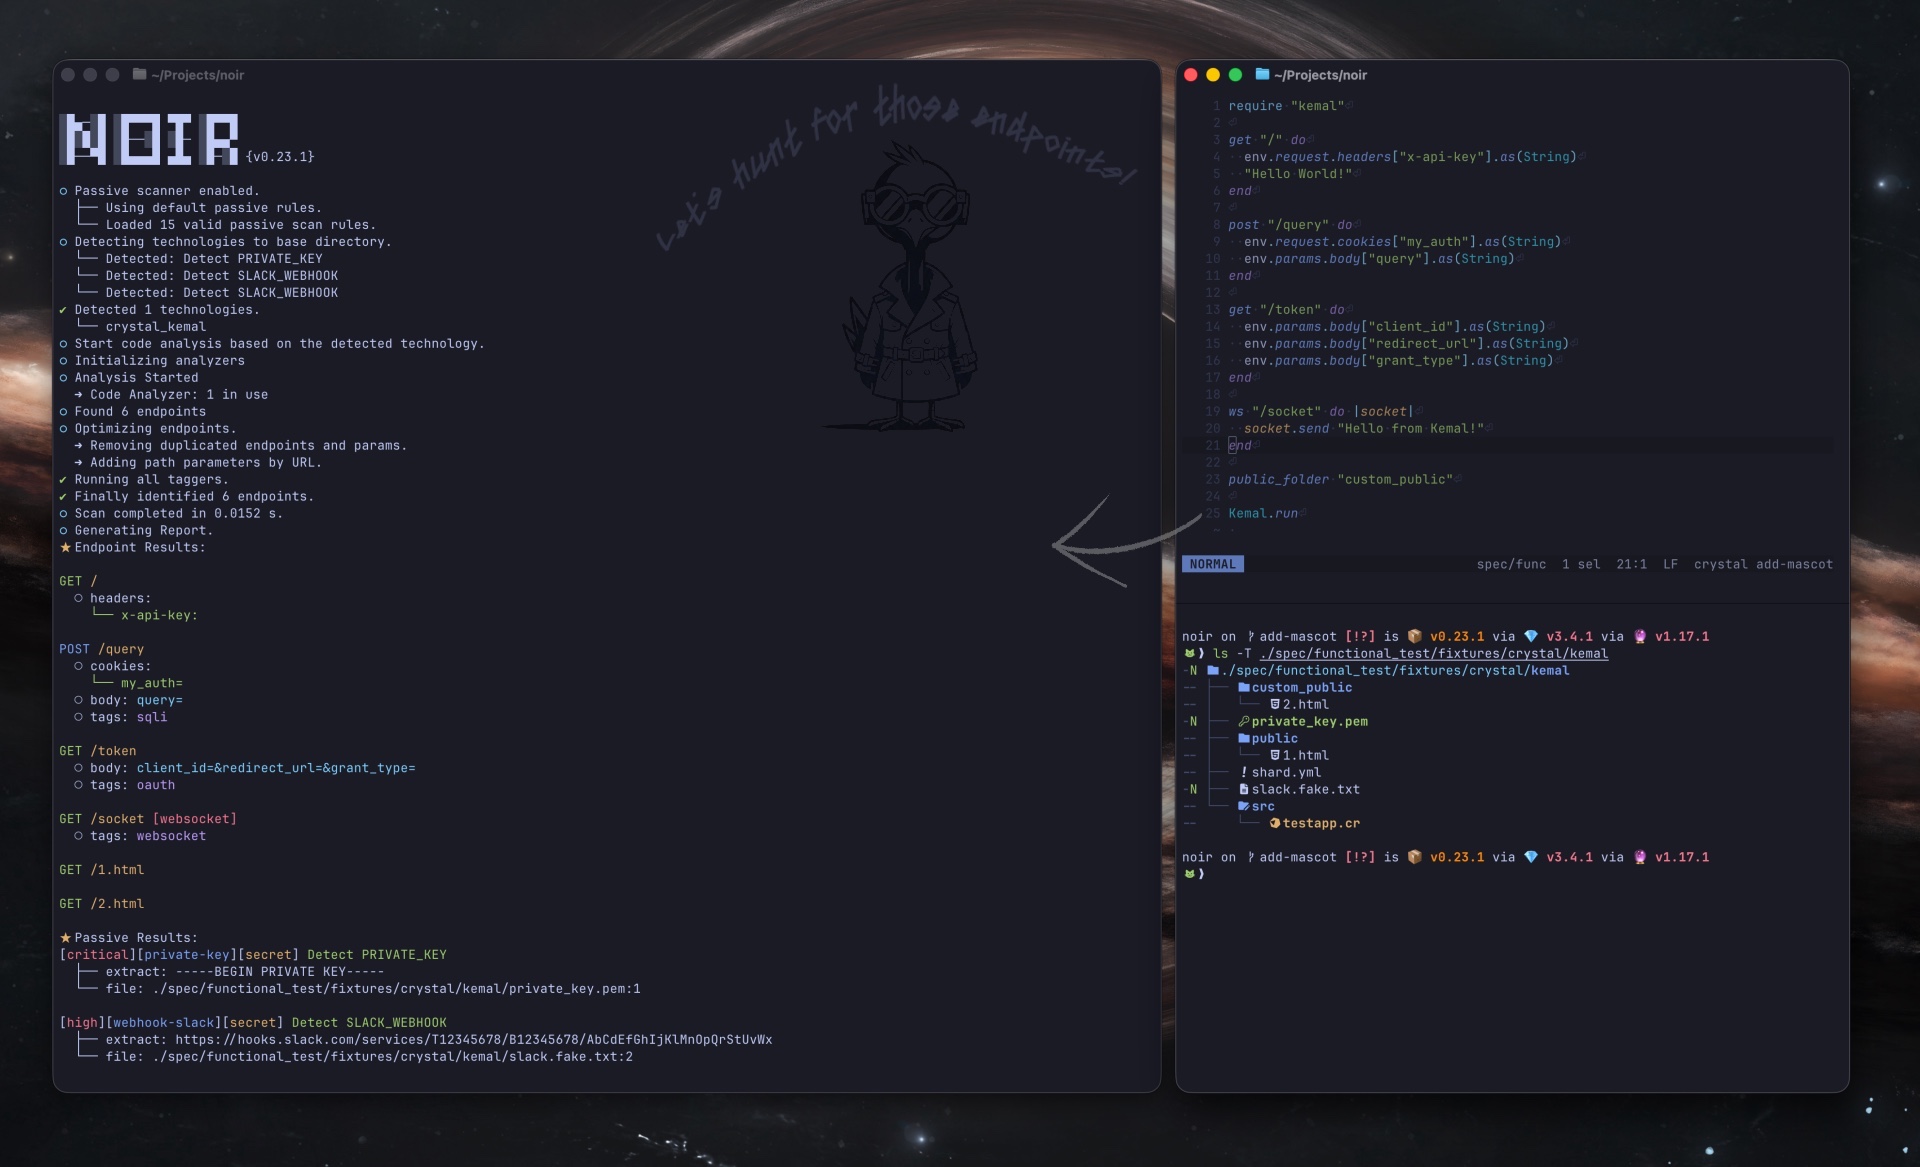
Noir is a SAST tool that reads source code and extracts the endpoints an application exposes — paths, methods, parameters, headers, cookies, and the source files behind them. Shadow APIs, deprecated routes, and undocumented handlers come out as part of the same inventory; they aren't a separate mode.
The inventory feeds three audiences:
- Human reviewers. Security engineers and code auditors get a focused list of attacker-reachable entrypoints — paths, parameters, source files, tags — instead of skimming the whole repo.
- AI auditors. LLM-based SAST agents get the same focused list, plus per-endpoint review context (
--include calleefor 1-hop callees,--ai-contextfor guards, sinks, validators, and signals). - DAST tools. ZAP, Burp Suite, Caido and Gori get a real route list to scan, including paths they would never have reached by crawling.
What Noir does
- Endpoint extraction. Static analysis across 205 frameworks. Returns endpoints, parameters, headers, cookies, and the source files they came from.
- LLM fallback. Hand unsupported frameworks (or one-off custom routing) to OpenAI / Ollama / etc. when static rules don't apply.
- Output for the next stage. JSON, YAML, OpenAPI, SARIF, cURL, Postman, HTML — whichever format the next tool in the pipeline reads.
- DAST integration. Pipe directly into ZAP, Burp Suite, Caido or Gori as a proxy target, or export OpenAPI for them to import.
- AI SAST context. The endpoint inventory (and, with
--include callee, the 1-hop functions each handler invokes) is the focused context an LLM auditor needs to find attacker-reachable bugs.--ai-contextgoes further and attaches aggregated review context per endpoint — guards, callees, sinks, validators, and signals — so the LLM doesn't have to rediscover them. - CI/CD. GitHub Action, SARIF output, exit codes — fits the pipeline you already have.
Usage
noir -hExample
noir -b <source_dir>If you use it with Github Action, please refer to this document .
For more details, please visit our documentation page.
Roadmap
Noir started as a WhiteBox testing aid: extract endpoints from source so DAST can scan them more accurately. The job has grown — the same inventory now feeds human auditors and AI SAST agents too. The goal from here is to serve all three consumers equally well: humans reviewing the code, LLMs auditing it, and DAST tools scanning it.
From here:
- Broaden language and framework coverage; keep accuracy honest with per-framework fixtures.
- Lean harder on LLMs for the cases static analysis can't reach.
- Enrich the per-endpoint review context (guards, callees, sinks, validators, signals) so human reviewers and AI auditors share the same focused view of each handler.
- Keep DAST integration first-class — OpenAPI, proxy targets, and direct hand-offs to ZAP / Burp / Caido.
OWASP Project
OWASP Noir joined the OWASP Foundation in June 2024.
- Official project page: https://owasp.org/www-project-noir/
- OWASP Nest: https://nest.owasp.org/projects/noir
News & Updates
- May 2026: Released v1.0.0 — introducing a stable 1.x line across all analyzers, taggers, passive-scan, and a brand new verb-centric CLI structure.
- May 2026: Refreshed the roadmap — Noir's goal is now to serve humans, AI auditors, and DAST tools equally as consumers of the same endpoint inventory.
- August 2025: Presented at the OWASP Seoul Meetup. (Open Source Gardening)
- November 2024: Published a guest blog post "Powering Up DAST with ZAP and Noir" on the ZAP blog.
- June 2024: Joined OWASP as OWASP Noir
- Renamed the GitHub organization from noir-cr to owasp-noir
- Transitioned to co-leadership with @ksg97031
- November 2023: Moved the Noir repository to the noir-cr GitHub organization.
- August 2023: Started as @hahwul's personal project.
Core Team
Contributing
Noir is an open-source project made with ❤️. If you would like to contribute, please check CONTRIBUTING.md and submit a Pull Request.
Mascot
 | Our mascot is Hak (학), a crane symbolizing elegance and precision in spotting hidden flaws. In Korean, "학" means "crane," representing a sharp ally who dives deep to uncover vulnerabilities and attack surfaces in your code. For more artwork and resources related to Hak, check out noir-artwork repository. |
|---|
API
- AIContext
- AIContextEntry
- AccountRecoveryTagger
Flags credential-management and account-recovery endpoints — password reset/change, forgot-password, email change, MFA/2FA enrollment, OTP, and account verification/recovery.
- AdminTagger
Flags administrative / privileged endpoints.
- Analyzer
- AnalyzerExample
Template for a new framework adapter (layer L2).
- AnalyzerFailure
Coverage a tech analyzer did not deliver, named so the scan can say which part of the code base it never actually looked at.
- ApiDocsTagger
Flags API documentation / schema endpoints — Swagger UI, OpenAPI/JSON specs, GraphiQL, ReDoc, RapiDoc, WSDL/WADL, Spring
…/api-docs. - AspnetAuthTagger
- AtomicFlag
Reference-typed atomic Boolean.
- Callee
A function/method invoked directly from an endpoint's handler body (1-hop only).
- CliEndpointSupport
Shared by the 21
src/analyzer/analyzers/{lang}/cli.cranalyzers, which all build the same thing: a set ofcli://<binary>endpoints, one per (sub)command, so that flags and env vars discovered in different files merge onto one command. - CodeLocator
- ConfigInitializer
- CorsTagger
- CryptoTagger
Flags endpoints that perform cryptographic operations — encryption / decryption, signing / verification, hashing, or key management.
- CrystalAuthTagger
- CurlCommand
Shared curl command construction used by the curl output builder and the HTML report's copy-as-curl feature.
- DebugTagger
Flags debug, diagnostic, and internal-only endpoints — debug consoles and toggles, profilers, Spring Boot Actuator, Go
net/http/pprof, heap/thread dumps,phpinfo, and/internalAPIs. - Deliver
- Details
- Detector
- DjangoAuthTagger
- ElixirAuthTagger
- Endpoint
- EndpointOptimizer
Endpoint optimization module that handles endpoint deduplication, URL combination, and path parameter extraction
- EndpointReference
- ExpressAuthTagger
- FastAPIAuthTagger
- FastEndpointsAuthTagger
- FileAnalyzer
- FileHelper
- FileScanEngine
Base for engines whose scan is "walk the language's source files and extract endpoints from each independently".
- FileUploadTagger
- FlaskAuthTagger
- FrameworkTagger
- GoAuthTagger
- GoRouteGroupScope
Shared Go route-group scope resolution for the Go framework taggers.
- GoSecurityTagger
Go security-middleware tagger.
- GolangLexer
- GraphqlTagger
- HonoAuthTagger
- HtmlReportAssets
The Noir brand mark (docs/static/images/logo-s.png) embedded as base64 so the report stays a single self-contained file.
- HuntParamTagger
- InternalGraphqlParser
Parses GraphQL operation documents (`query Foo { ...
- JavaMiscAuthTagger
- JsMiscAuthTagger
- JwtTagger
- KtorAuthTagger
- LLM
- LLMEndpointOptimizer
Enhanced optimizer with LLM-based optimization capabilities for refining non-standard or unconventional paths and parameters
- McpTagger
- MediaFilter
- MiniLexer
- MobileLaunch
Helpers shared by the mobile launch-command builders (adb, simctl).
- NestjsAuthTagger
- Noir
Part of Noir::TreeSitterKotlinRouteExtractor: WebFlux functional router DSL (coRouter/router blocks).
- NoirAIContext
NoirAIContext enriches each endpoint with an
AIContext— the guards / callees / sinks / validators / signals an LLM (or a human triage pass) needs to reason about the route. - NoirLogger
- NoirMobileLinker
Post-analysis pass that links mobile deep-link endpoints (produced by the config-file analyzers from AndroidManifest.xml) to the source code that handles them.
- NoirOutputFiles
Process-wide registry of
-ofile handles, one per output path. - NoirPassiveScan
- NoirRunner
- NoirTaggers
- NoirTechs
- OAuthTagger
- OutputBuilder
- OutputBuilderAdb
Emits
adb(Android Debug Bridge) commands that launch the Android entry points Noir discovers — custom-scheme deep links, verified app links, explicit intent components, and content providers — on a connected Android device or emulator. - OutputBuilderCommon
- OutputBuilderCurl
- OutputBuilderDiff
- OutputBuilderHtml
- OutputBuilderHttpie
- OutputBuilderJson
- OutputBuilderJsonl
- OutputBuilderMarkdownTable
- OutputBuilderMermaid
- OutputBuilderOas2
- OutputBuilderOas3
- OutputBuilderOasCommon
- OutputBuilderOnlyCookie
- OutputBuilderOnlyHeader
- OutputBuilderOnlyParam
- OutputBuilderOnlyTag
- OutputBuilderOnlyUrl
- OutputBuilderPassiveScan
- OutputBuilderPostman
- OutputBuilderPowershell
- OutputBuilderSarif
- OutputBuilderSimctl
Emits
xcrun simctl openurlcommands that open the iOS entry points Noir discovers — custom-scheme deep links and verified universal links — on a booted iOS Simulator. - OutputBuilderToml
- OutputBuilderTomlSerializer
TOML emission shared by the
-f tomlbuilder and diff mode'sprint_toml. - OutputBuilderYaml
- Param
- ParserLimit
Parser limits from environment (e.g.
- PassiveRulesUpdater
- PassiveScan
- PassiveScanResult
- PassiveScanSeverity
- PathInfo
- PaymentTagger
Flags payment / financial transaction endpoints.
- PerlAuthTagger
Identifies authentication / authorization guards in Perl web apps.
- PhpAuthTagger
- PiiTagger
Flags endpoints that accept personally identifiable information (PII) or other sensitive personal data.
- PrefixScope
Segment-aware URL-prefix containment, shared by every framework tagger that resolves a scoped middleware registration ("this guard covers prefix P — does it cover endpoint U?").
- ProbeConcurrency
Max concurrent in-flight probe requests, shared by every class that fires requests at discovered endpoints.
- PythonMiscAuthTagger
- PythonParser
Python source-file parser used by the Flask analyzer to resolve routing-relevant globals (Blueprint / Namespace / Api instances) across files.
- RailsSecurityTagger
Rails-specific security tagger.
- RubyAuthTagger
- RustAuthTagger
- RustSecurityTagger
Rust-specific security tagger.
- SampleLexer
- ScalaAuthTagger
- SendElasticSearch
- SendReq
- SendWebhook
POSTs the discovered endpoint catalog as a single JSON document to a user-supplied webhook URL.
- SendWithProxy
- SoapTagger
Flags SOAP / XML web-service endpoints.
- SourceContext
- SpringAuthTagger
- SpringPropertyPath
Resolves Spring
${property:default}placeholders in any mapping path. - SpringSecurityTagger
Spring-specific security tagger.
- StatusCodeProbe
Fills in
details.status_codefor every endpoint (--status-codes) and drops the ones whose code the user excluded (--exclude-codes). - String
Extend ::String class to check if a string is numeric
- SwiftAuthTagger
- Tag
- Tagger
- Tnetstring
Tnetstring decoder used by the mitmproxy flow analyzer.
- Token
- WebhookTagger
Flags inbound webhook / callback endpoints — routes that receive server-to-server notifications from third parties (payment providers, VCS hosts, CI, messaging platforms).
- WebsocketTagger
Flags WebSocket endpoints — long-lived, bidirectional channels whose threat model (origin checks on the handshake, per-message authz, no CSRF token on the upgrade) differs from a request/response route.